Customer Privacy Protection
Personal Data and Privacy Protection Policy
FET follows the domestic laws and regulations, including the Personal Data Protection Act, the Enforcement Rules of the Personal Data Protection Act, and the NCC's regulations on non-public agencies' personal data file security maintenance. Additionally, the company referred to the General Data Protection Regulation (GDPR) of the European Union to ensure the protection of privacy information. FET adheres to fundamental principles such as Privacy by Design and Data Protection by Design to safeguard privacy information.
FET's Privacy Policy applies to the entire operational process of FET, including suppliers and partners. All employees of FET are required to comply with the "Management Regulations for Personal Data and Privacy Information Collection, Processing, and Utilization" set by the company. When collecting personal data and privacy information, it must adhere to the approved collection purposes and scope, and inform the data subjects about the collection. If any employee is found to violate the relevant policies and regulations, FET will take necessary disciplinary actions according to the code of conduct and may implement relevant legal measures as appropriate. For details, please refer to FET's Privacy Policy on official website
Information Security and Privacy Management Organization
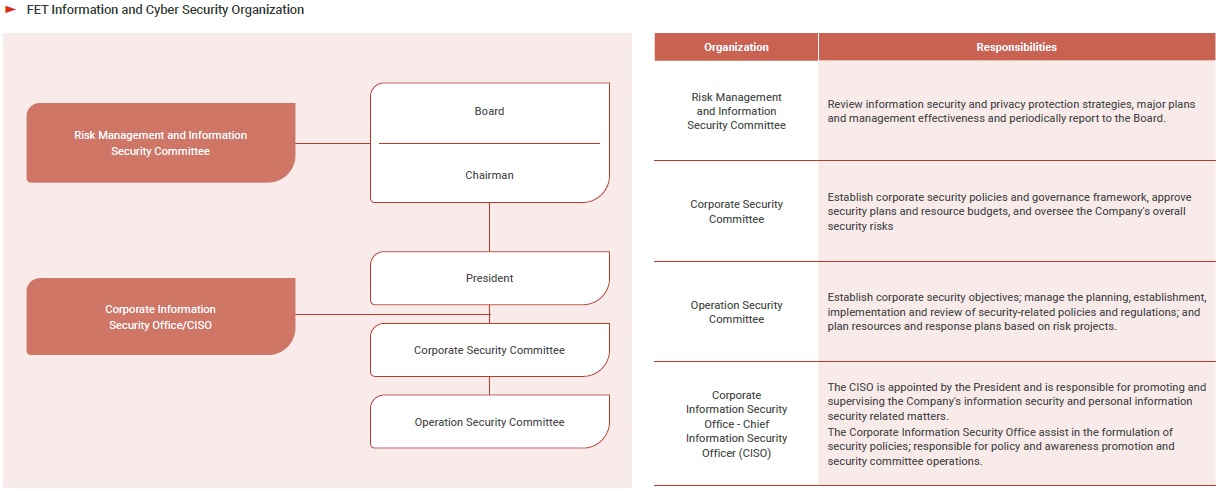
To demonstrate its emphasis on and commitment to information security and customer privacy, FET has established a information security organization. Furthermore, the Board of Directors resolved to renaming the “Risk Management and Information Security Committee” (RMC) to “Risk Management and Information Security Committee” (RMSC) on May 03,2024, to regularly review the information security and privacy protection strategies, key projects, and management effectiveness. The management organization has more than 30 members including the President and the representatives from all business units. In addition, FET has set up a dedicated security department - Corporate Information Security Office and Chief Information Security Officer (CISO). The CISO is assigned and directly reports to the President. Through various committees, FET promotes and advocate for information security and personal data privacy affairs within each business unit. FET also coordinates responsibilities and tasks related to security maintenance across business units to ensure the comprehensive implementation and operation of information security throughout the entire company.
Information Security and Risk Management Mechanisms
In response to the new wave of digital transformation driven by emerging technologies such as 5G, Big Data, AI, IoT, and cloud/virtualization/container technologies, FET recognizes that the integration of new services, architectures, and technologies with existing networks—as well as cross-sector and cross-industry collaborations with third parties—introduces new challenges to information security and personal data protection. Building on its existing security management foundation, FET continuously strengthens its technical, managerial, and personnel protection mechanisms across network infrastructure, operations, and management. The company dynamically allocates resources based on evolving demands to ensure effective information security, personal data protection, business continuity, and the implementation of other security-related governance measures.
To provide secure and optimal user experience, FET has independently developed an intelligent monitoring platform equipped with multi-dimensional visualization dashboards and customized threat detection rules. This platform enables more accurate identification of security risks and supports preemptive defense by detecting and blocking threats before potential attacks are launched. FET also maintains a dedicated cybersecurity protection team and a 24*7 Security Operations Center (SOC), staffed by certified professionals with more than 10 years of experience and certifications such as CEH (Certified Ethical Hacker). Various security assessments—including vulnerability scanning, source code review, and penetration testing—are conducted regularly. Identified vulnerabilities are required to be remediated within a prescribed timeline and must pass follow-up testing.
FET’s information security monitoring framework covers four major control domains: Information and Technology Security, Personnel Security, Physical and Environmental Security, and Customer Personal Data Protection. The key control focuses for each domain are outlined as follows:
Information and |
Personnel Security |
Physical and |
Customer Personal |
|
|
|
|
Data collection and preservation
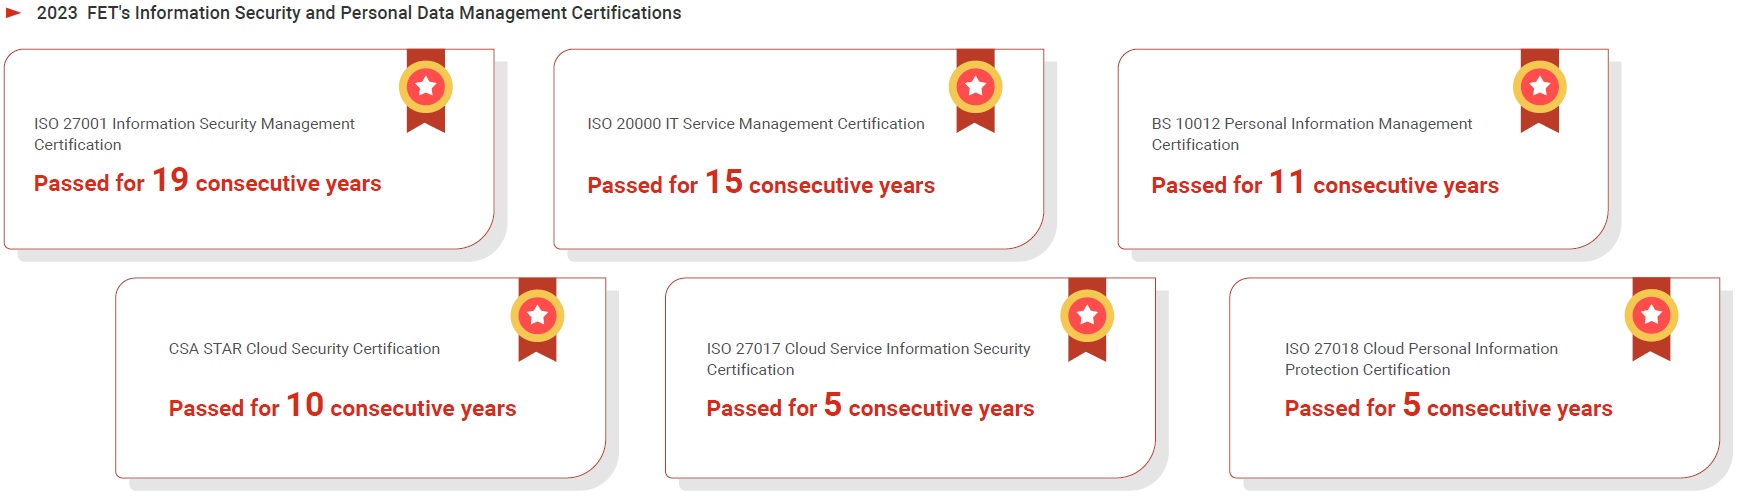
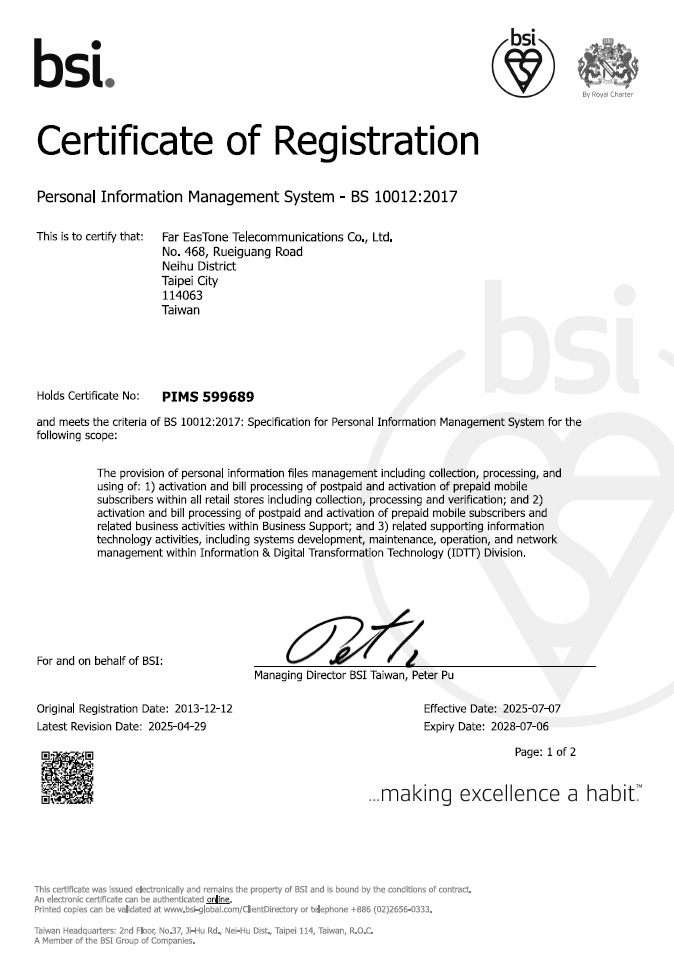
FET Telecom primarily collects customer personal information through physical retail stores, telemarketing channels, and other means. At the time of collection, customers are informed of the purpose and scope of the personal data and privacy information being collected. Upon reviewing the notification, customers are required to provide the personal data necessary to apply for mobile broadband and value-added telecom services via the service application form and to consent to the stated data collection terms. Regarding data retention, FET Telecom follows applicable legal and contractual requirements, and egularly reviews the necessity of retaining personal information. When the retention period expires or the original purpose of data collection no longer applies, FET Telecom will either proactively determine or act upon the individual’s request to destroy or delete the data. Such deletion is executed in a manner that ensures the data is irretrievable and unidentifiable. FET Telecom has maintained BS 10012 certification for 13 consecutive years. The scope of certification includes data collection at retail stores across Taiwan for customer subscription applications, and back-end operations such as billing, invoice mailing, and data processing activities.
Data processing and utilization
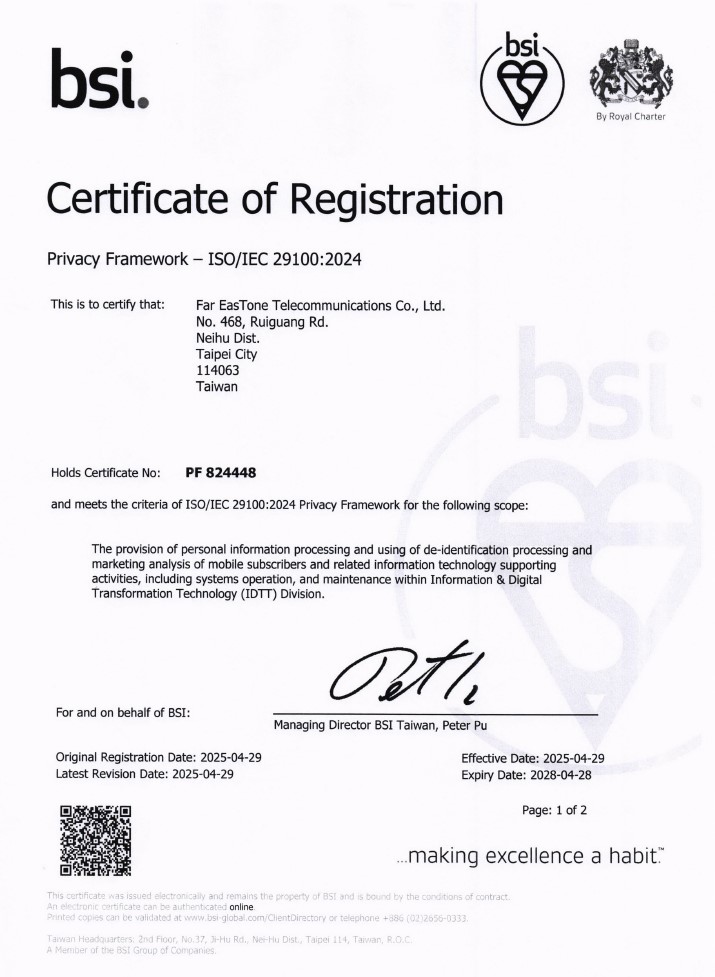
Regarding the handling and utilization of personal data and privacy information, FET Telecom strictly follows regulations within the scope defined by data collection and user consent. As of the end of 2025, 76.9% of customers have agreed to the use of their data for incidental purposes. Unless informed and consented by the data subject or required by law, personal data and privacy information should not be processed or utilized by third-party organizations or individuals. In terms of maintaining information file security, FET Telecom has established guidelines based on the life cycle of user personal data and privacy information. The company rigorously implements identity verification and access authorization, layered privacy protection, data minimization, and limited use of data for operational necessity. Data is also de-identified, and outputs are blurred (by ranges, aggregated statistics), with disclosure restrictions (minimum number of individuals in grid cells) to enhance information security and reduce privacy risks.
Complaint channels and legal review procedures
FET Telecom has established a toll-free customer service hotline (0800-058-885) to handle customer requests, complaints, and inquiries related to personal data. Customers with privacyrelated concerns may file a grievance through the customer complaint mechanism, and FET Telecom will address the issue promptly. When necessary, the Corporate Information Security Office will convene an emergency response team to investigate the incident. In compliance with the Telecommunications Act and other relevant regulations, telecom operators in Taiwan are required to provide user information and call detailed records to government authorities upon lawful request. To manage such inquiries, FET Telecom has formulated the “Standard Operating Procedure for the Retrieval of Call Detail Records, Basic Information, and Emergency Assistance Requests.” The company responds to these requests using secure and encrypted methods and maintains complete records for auditing purposes.
In 2025, FET Telecom received 3 complaints from regulatory authorities concerning customer privacy leaks. Investigations revealed that these cases stemmed from public misunderstandings regarding the identity verification process during subscription applications, and there were no violations of customer personal data or privacy-related laws, nor any resulting financial losses. Additionally, a total of 253,731 official requests for customer information were received from government agencies in 2025 in accordance with legal requirements, and all were handled following the company’s statutory procedures. To address concerns regarding unauthorized data transmission or misuse of privacy information, FET Telecom actively promotes awareness of personal data protection across all departments, enforces traceability in operational processes, and strengthens internal procedures for data verification and authorization as part of its proactive risk response framework.